Ask most people what database security means, and they’ll say passwords and access rules. Fair enough, but it’s only half of it. You can lock down logins perfectly and still be exposed if the engine underneath is running a vulnerable version. On October 15, 2026, AWS published a notice about CVE-2026-110812, an Amazon Neptune Gremlin vulnerability. AWS has released patched engine versions and recommends that affected customers upgrade. The CVE-2026-110812 fix is available in Neptune engine versions 1.4.7.1, 1.4.8.1, and 1.5.0.0. If you’re running Neptune, check your engine version and review who can send queries to your clusters. You can find the details in the official AWS security bulletin. What Is the Amazon Neptune Gremlin Vulnerability? Neptune is Amazon’s managed …
A critical vulnerability, CVE-2026-98432, has emerged within the IPv4 TCP networking stack of the Linux kernel, prompting urgent attention from hosting providers, system administrators, and DevOps professionals. Rated with a CVSS score of 9.8, this critical Linux kernel vulnerability stems from a use-after-free condition. An unauthenticated remote attacker can potentially trigger kernel memory corruption, resulting in a complete system crash or, under certain conditions, remote code execution (RCE). The critical concern is that this Linux TCP vulnerability extends beyond individual Linux distributions or specific applications, as it resides within the fundamental code responsible for IPv4 TCP connection handling. Consequently, any server running an affected kernel build may remain exposed, regardless of the hosting control panel or applications installed. For administrators …
If your 2027 plans depend on partnerships you haven’t built yet, November is the right time to start building them. In the hosting and cloud industry, most partnerships start with a conversation, not a contact form. A well-timed meeting at an industry event can open doors that months of emails rarely do. That’s the opportunity at CloudFest Americas 2026, and we’re pleased to share that the SupportPro team will be attending. In this guide, we cover what’s happening in Miami, who the event is for, and what you can gain from attending. What is CloudFest Americas 2026? CloudFest Americas 2026 is a two-day internet infrastructure festival on November 11-12, 2026, at Ice Palace Studios in Miami, Florida. It brings together …
PHP2Shell: What cPanel, Plesk, DirectAdmin, and CWP Administrators Must Check Now?
PHP security updates should be a priority for hosting administrators after the disclosure of two critical vulnerabilities known as PHP2Shell. Tracked as CVE-2026-109618 and CVE-2026-109619, these vulnerabilities affect PHP’s core runtime and can allow unauthenticated attackers to execute code remotely on vulnerable servers. Both vulnerabilities carry a CVSS v4.0 score of 9.2. Security authorities have also reported exploitation in the wild, making this an issue that requires immediate attention. For hosting providers, updating a single PHP installation is not enough. A server may have several PHP versions installed, with different websites using different handlers and configurations. First, identify every PHP runtime serving web requests, verify its security status, and apply the appropriate vendor updates. This includes PHP-FPM, Apache mod_php, CGI, …
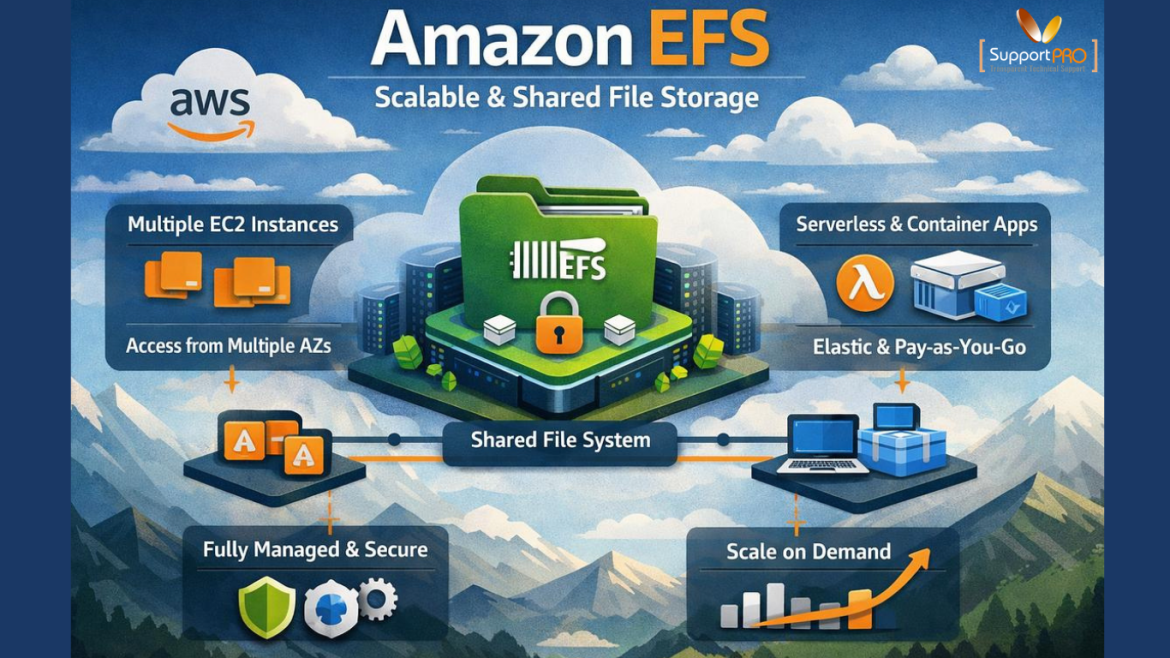
Linux administrators must keep more than the operating system kernel up to date. Supporting packages that handle storage, networking, and cloud integrations also need regular maintenance.On October 28, 2026, AWS released security advisory ALAS2-2026-4044 for CVE-2026-15957, a vulnerability affecting the amazon-efs-utils package on Amazon Linux 2. AWS classifies the advisory as Important and identifies amazon-efs-utils-3.1.3-1.amzn2 as the corrected package. The vulnerability involves uncontrolled recursion in Smithy-RS-generated deserialization functions. Deeply nested data can exhaust the stack and cause a process to abort, creating a denial-of-service (DoS) risk. Administrators should identify affected instances, update the package, and verify that applications using Amazon Elastic File System (EFS) continue to work. What Is the Amazon Linux 2 EFS Utilities Update? The amazon-efs-utils package provides …
AI Coding Agent Security: How Malicious AGENTS.md Files Can Hijack AI Workflows
AI coding agents can do more than suggest code. Depending on their permissions, they can read project files, run terminal commands, install packages, change configuration, and call external services. That speed creates a new security boundary: AI coding agent security agents may act on instructions found in files that nobody has reviewed. As the AI coding agent plugin vulnerability CVE-2026-107322 showed earlier this month, the tooling around these agents is already a target. On October 22, 2026, security company Forever Security said it discovered a malicious AGENTS.md file in a customer’s Downloads folder. The researchers also reproduced attack chains involving OpenAI Codex and Claude Code during controlled testing. Their investigation showed how an ordinary-looking instruction file could potentially steer an …
What Hosting Administrators Need to Know A Linux server can run websites smoothly and still have a serious flaw in its operating system. That’s why hosting providers need to pay attention to kernel vulnerabilities, even when their applications and customer accounts appear to work normally. One recent example is ZDI-CAN-33367, a Linux kernel vulnerability that allows a local, unprivileged user to change file contents stored in memory under specific conditions. The affected file may belong to another user or even root, although the attacker normally can read it but not modify it. The vulnerability can create a serious problem for hosting providers that run multiple customer accounts on the same server. If an attacker gains local access, they may use …
Picture a new apartment building. Before anyone moves in, an inspector checks every lock and window. That’s image scanning. It tells you what could go wrong.. But what if someone is already jiggling a door handle at 2 a.m.? That’s where Kubernetes runtime security comes in. It’s the smoke alarm: it spots trouble while it’s happening. On 16 October 2026, Google announced a preview of the Wiz Runtime Sensor as a managed add-on for Google Kubernetes Engine (GKE). It covers both Standard and Autopilot clusters. The big idea: GKE installs and updates the sensor for you, instead of a Helm release you babysit across dozens of clusters. If you run Kubernetes for a SaaS product or manage clusters for clients, …
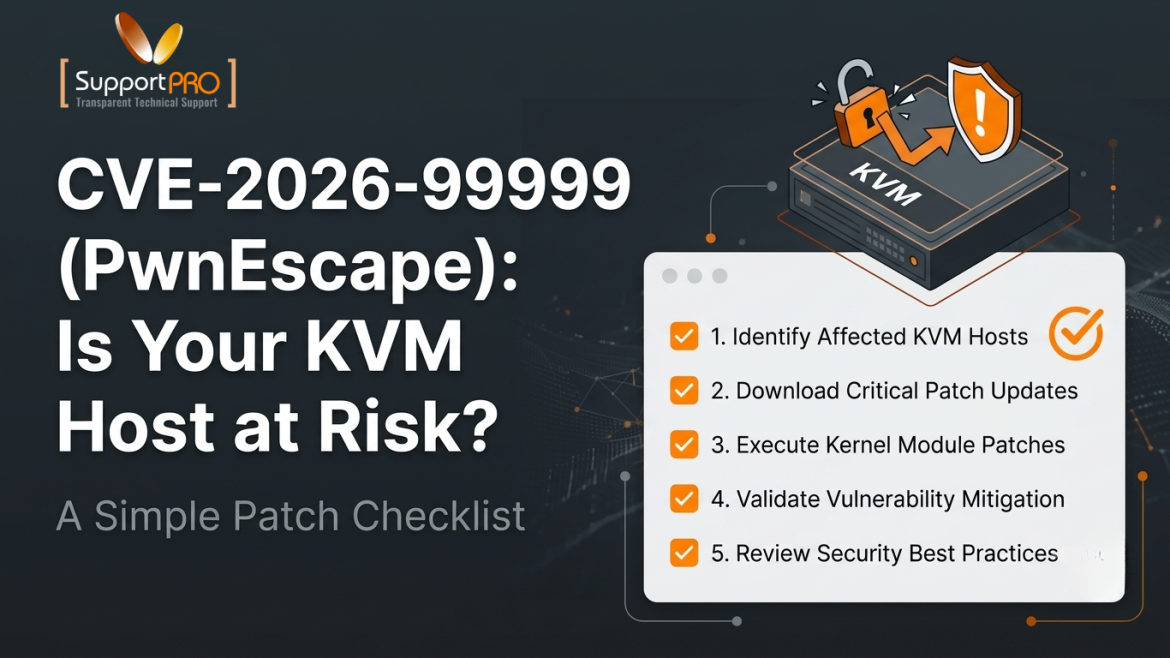
Picture an apartment building. The building is your server. Each apartment is a virtual machine (VM) that you rent to a customer. Most tenants are lovely. A few are curious. And once in a while, one of them finds a way to walk through the wall into the building’s control room. That is the kind of problem CVE-2026-99999 creates. Researchers call it PwnEscape. It is a flaw in the Linux kernel, in the part that handles virtio-net and TAP networking. AWS published a bulletin about it (2026-137-AWS) on October 15, 2026, and advice from different vendors keeps changing as new details emerge. This checklist is for VPS providers, data centers, and businesses that run their own KVM hosts. By the …
PHP CVE-2026-109618 and CVE-2026-109619: What Hosting Teams Should Do Now?
PHP CVE-2026-109618 and CVE-2026-109619 are critical remote code execution vulnerabilities disclosed on October 21, 2026. Both vulnerabilities could allow attackers to execute code on affected PHP servers without authentication. PHP has released patched versions, so hosting providers should identify vulnerable installations and apply the appropriate updates promptly. Updating WordPress, plugins, and themes alone does not protect a website from vulnerabilities in the underlying PHP runtime. If a server still runs a vulnerable PHP version, the website may remain at risk even when its applications are fully updated. For web hosting companies, fixing these vulnerabilities requires more than updating a single server. One server may run multiple PHP versions, several PHP-FPM pools, and hundreds of customer websites. Hosting environments may also …