The International Earth Rotation & Reference Systems Service (IERS) has mentioned that an extra second is to be added to Coordinated Universal Time (UTC) at 23:59:59 on 30 June 2015 and this is to make sure the alignment of astronomical and atomic time. Coordinated Universal Time, UTC is one of the basic time conventions used by most of the world’s local time zones. This UTC time convention has been derived from a bunch of atomic clocks that are distributed across several countries globally. The rotation of our earth is not so constant and it changes a bit over time and in-turn it decreases the mean rotation speed slowly. This is the exact cause behind leap seconds that gets added up …

The VENOM vulnerability, also known as the QEMU virtual machine exploit, is a critical security flaw discovered on May 13, 2015 by security researcher Jason Geffner during a security review of virtual machine hypervisors. VENOM stands for Virtualized Environment Neglected Operations Manipulation and affects virtualization environments that rely on the QEMU emulator. What Is the VENOM Vulnerability? VENOM (CVE-2015-3456) is a virtual machine escape vulnerability located in the Virtual Floppy Disk Controller (FDC) code used by QEMU. Many popular virtualization platforms depend on QEMU components, including: If successfully exploited, the vulnerability allows an attacker to: This makes VENOM particularly dangerous in shared hosting and cloud infrastructures. How the VENOM Exploit Works The flaw exists in the emulated floppy drive functionality …
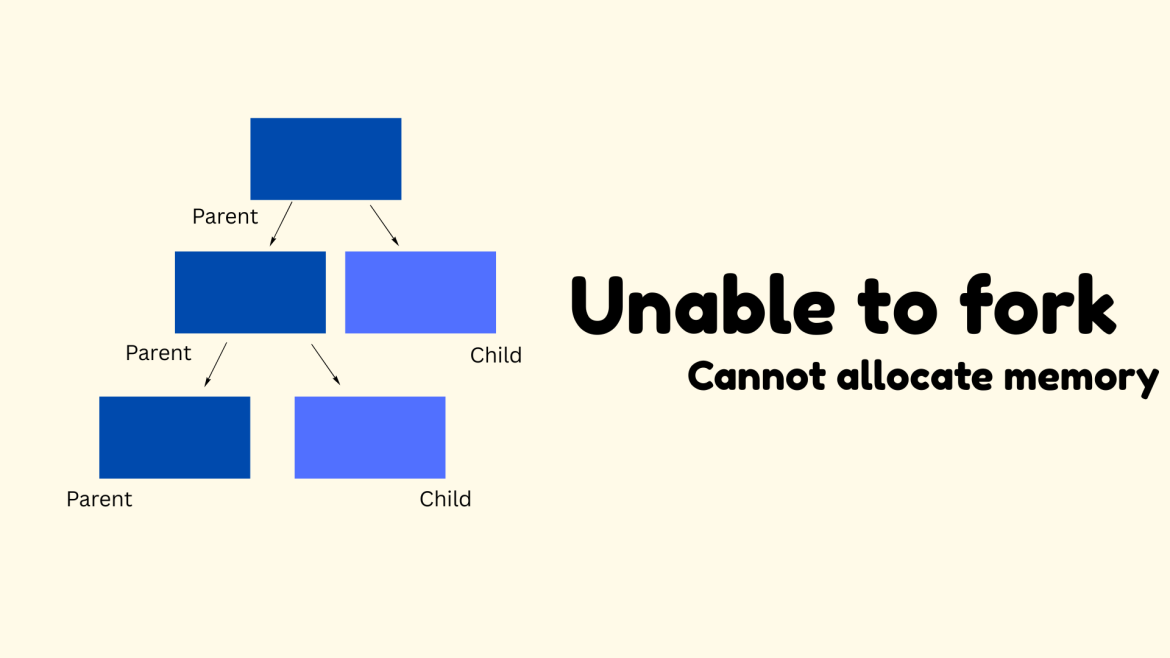
Issue Description While trying to access an OpenVZ container using the following command: you may encounter this error: Here, 10524 refers to the container ID. Step 1: Check Node Memory Availability First, verify whether the host node is running out of memory: If the system shows sufficient free memory, the issue is likely not at the node level. Step 2: Check Resource Limits (privvmpages) If memory is not the issue, the problem is usually related to OpenVZ memory limits, especially privvmpages. Check current resource usage: This file contains resource usage and limits for all containers. Step 3: Identify the Problem Container Locate the entry for container 10524 and check the privvmpages values: Then the container has hit its memory limit. …
Introduction Server security vulnerabilities can expose key services and applications to attacks. One of these vulnerabilities is the GHOST vulnerability (CVE-2015-0235). This flaw was found in the GNU C Library (glibc) and impacts many Linux distributions. Since several essential services, such as SSH, Bash, and DNS-related applications, rely on glibc, it is crucial for system administrators to check if their servers are vulnerable and implement the necessary fixes. This article outlines how to check for the GHOST vulnerability and decide if your Linux server is at risk. On Linux servers, more than 60 binaries and major services, such as SSH, Nmap, and Bash, rely on the glibc libraries. A heap-based buffer overflow was found in __nss_hostname_digits_dots(), and an attacker could …
The Config Server Mail Queue is an addon feature available with cPanel/WHM which provides with a full-featured interface to the cPanel exim email queues from within WHM. The add-on feature provides with an interface to the cPanel user accounts email configuration without having to log in to their accounts. It is domain-based rather than account-based. Features View, edit and delete email accounts, email forwarders and email filters. View and modify email account quotas Modify email account passwords List only email accounts that are over quota Modify Outgoing Mail Hourly Limits List only email accounts that are over a specified size View the total number of emails in an email account Empty an email account View emails in an email account …
Wine makes it possible to run Windows programs alongside any Unix-like operating system, particularly Linux. Wine is an implementation of the Windows Application Programming Interface (API) library, acting as a bridge between the Windows program and Linux. When a Windows program tries to perform a function, Wine will translate that program’s instruction and make it suitable for Linux. The Wine development release 1.7.35 is now available. New features in this release: – Beginnings of support for OpenGL core contexts. – Initial support for glyph placement in DirectWrite. – Some more WBEM objects. – Various bug fixes.
Advanced Maryland Automatic Network Disk Archiver (AMANDA) is a powerful open-source backup solution designed to simplify enterprise backup management. It enables IT administrators to use a single master server to back up multiple systems across a network, including Linux, Unix, and Windows machines. AMANDA supports various storage options such as tape drives, disks, and optical media, making it a flexible choice for businesses of all sizes. Why Choose AMANDA Backup? AMANDA is widely adopted due to its ability to streamline and automate backup processes. Key advantages include: It is an ideal solution for organizations looking for a scalable and cost-effective backup system. Key Features of AMANDA Installing AMANDA Network Backup Installing AMANDA is straightforward on most Linux systems. Prerequisites Ensure …
FirewallD is a new firewall suite being introduced to Linux distribution. At present, the all-new popular CentOs 7 has it as the default firewall suite which in near future will be implemented in servers. FirewallD, as usual, was developed by the Fedora community and was implemented in the 20th version of the same. It is also being used in arch Linux and others till the date. FirewallD is a dynamic firewall, dynamic in the sense that any change in the firewall will be implemented as soon as the amendment is made. That is unlike the previous firewall suite (iptable) where no hard reset or restart is needed to implement the rule amended or included. Iptables is deprecated in the early …
Portsentry is a tool to detect port scans and log it. Once a host is targeted by an attacker, a port scan is almost always performed. PortSentry detects such scans by monitoring the unused ports on the host. Upon a connection attempt to one of the unused ports, PortSentry is alerted and has the ability to issue a number of commands in response to the scan. Installation # cd /usr/src/ # wget http://sourceforge.net/projects/sentrytools/files/latest/download
MariaDB is a high performance drop-in replacement for MySQL, developed by some of the original authors of the MySQL project. For years, MySQL has been the dominant open-source database management system (DBMS). Recently, MariaDB, the MySQL fork created by MySQL’s founder, has been making in-roads and websites like Wikipedia the world’s sixth most popular Web site, is shifting over from MySQL to MariaDB. Lets check how to replace MYSQL with MARIADB in a cpanel server Step 1: Backup existing MySQL data Before installing mariadb make sure to take backup of current mysql data